Repository navigation
feat(agents): per-agent environment variables - #4011
wpfleger96 wants to merge 15 commits into
Conversation


6a9d3b4 to
e7d643e
Compare

 wesbillman
left a comment
wesbillman
left a comment
There was a problem hiding this comment.
🤖 Star Lord’s source review of e7d643e recommends changes to agent launch, credential handling, and lifecycle cleanup. The per-agent feature also needs a core-team decision on whether individual harnesses should register support through a shared native capability. Runtime behavior remains unverified.

 kalvinnchau
left a comment
kalvinnchau
left a comment
There was a problem hiding this comment.
🤖 Three additional findings on restart ordering, damaged-list recovery, and API documentation. The cross-instance cleanup race is already covered by discussion_r4636997497.

Goose asks for the agent list only from a local agent's launch; a saved
per-agent Anthropic key survives Claude's env and counts as a credential;
the custom-header check reads the agent's launch env; a failed dedicated
Codex start is tracked until it exits; harness path variables are
rejected; Save keeps focus; Restart waits for a pending save; the
unreachable damaged-list replace is removed.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
Goose asks for the agent list only from a local agent's launch; a saved
per-agent Anthropic key survives Claude's env and counts as a credential;
the custom-header check reads the agent's launch env; a failed dedicated
Codex start is tracked until it exits; harness path variables are
rejected; Save keeps focus; Restart waits for a pending save; the
unreachable damaged-list replace is removed.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
02d46c7 to
a87d871
Compare
kalvinnchau
left a comment
kalvinnchau
left a comment
There was a problem hiding this comment.
🤖 Two remaining configuration-contract issues are noted inline.
Goose asks for the agent list only from a local agent's launch; a saved
per-agent Anthropic key survives Claude's env and counts as a credential;
the custom-header check reads the agent's launch env; a failed dedicated
Codex start is tracked until it exits; harness path variables are
rejected; Save keeps focus; Restart waits for a pending save; the
unreachable damaged-list replace is removed.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
6ff52cd to
501b5e3
Compare
kalvinnchau
left a comment
kalvinnchau
left a comment
There was a problem hiding this comment.
🤖 One remaining configuration-root omission; details inline.
Goose asks for the agent list only from a local agent's launch; a saved
per-agent Anthropic key survives Claude's env and counts as a credential;
the custom-header check reads the agent's launch env; a failed dedicated
Codex start is tracked until it exits; harness path variables are
rejected; Save keeps focus; Restart waits for a pending save; the
unreachable damaged-list replace is removed.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
501b5e3 to
1d433c4
Compare
Goose asks for the agent list only from a local agent's launch; a saved
per-agent Anthropic key survives Claude's env and counts as a credential;
the custom-header check reads the agent's launch env; a failed dedicated
Codex start is tracked until it exits; harness path variables are
rejected; Save keeps focus; Restart waits for a pending save; the
unreachable damaged-list replace is removed.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
498f798 to
7a1ff43
Compare
Goose asks for the agent list only from a local agent's launch; a saved
per-agent Anthropic key survives Claude's env and counts as a credential;
the custom-header check reads the agent's launch env; a failed dedicated
Codex start is tracked until it exits; harness path variables are
rejected; Save keeps focus; Restart waits for a pending save; the
unreachable damaged-list replace is removed.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
7a1ff43 to
0c02538
Compare

|
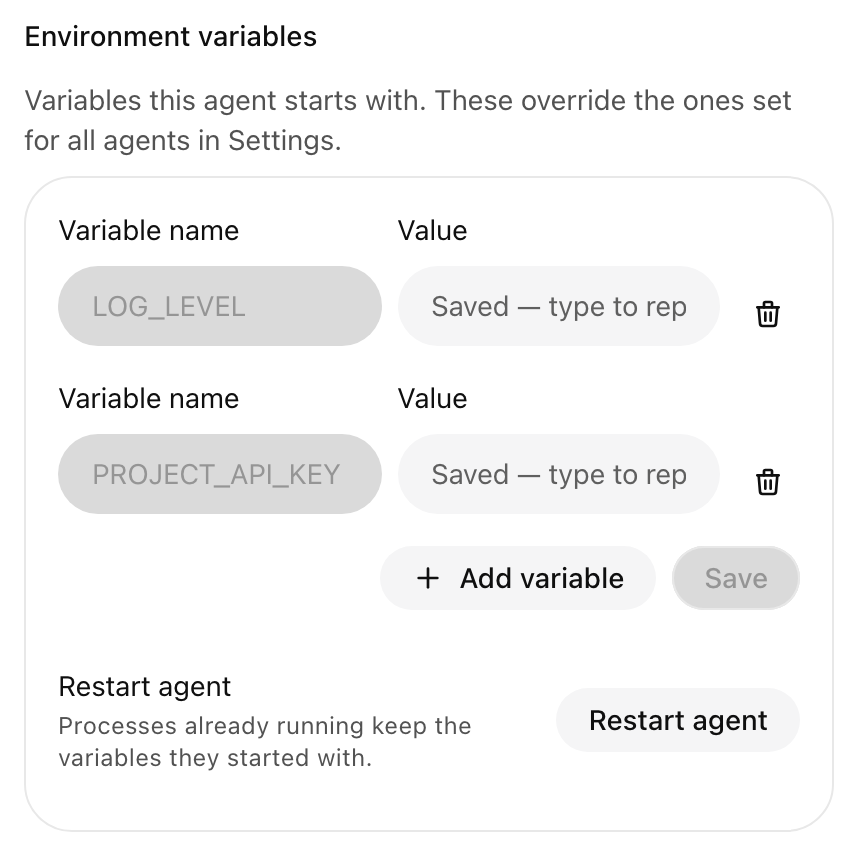
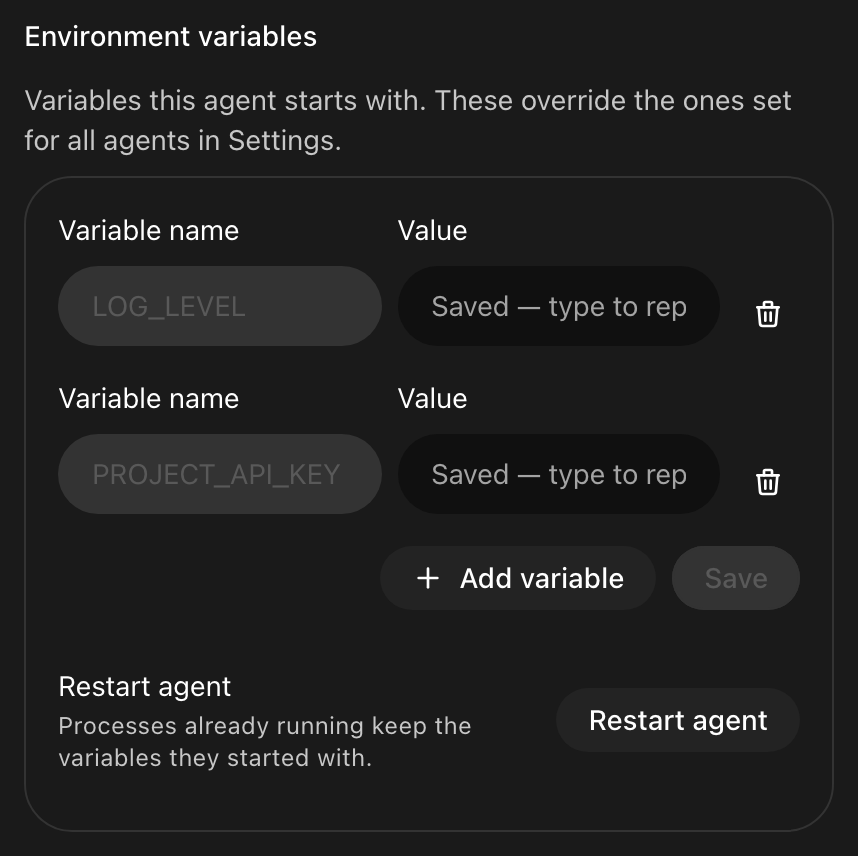
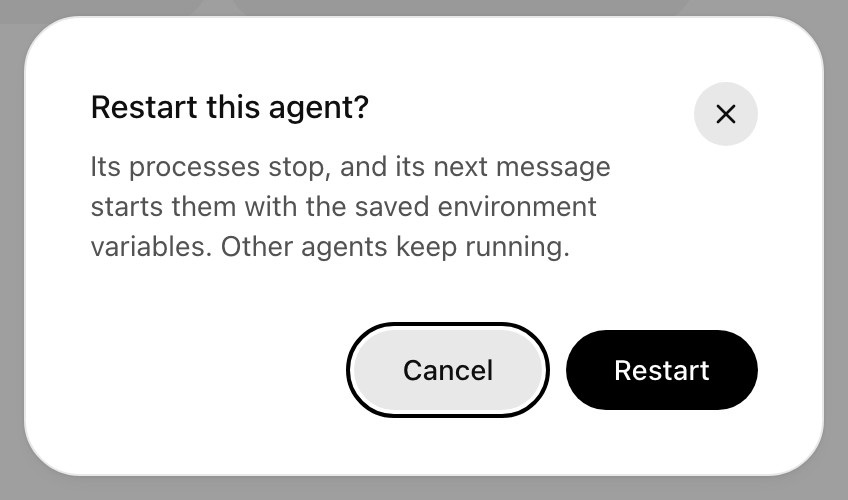
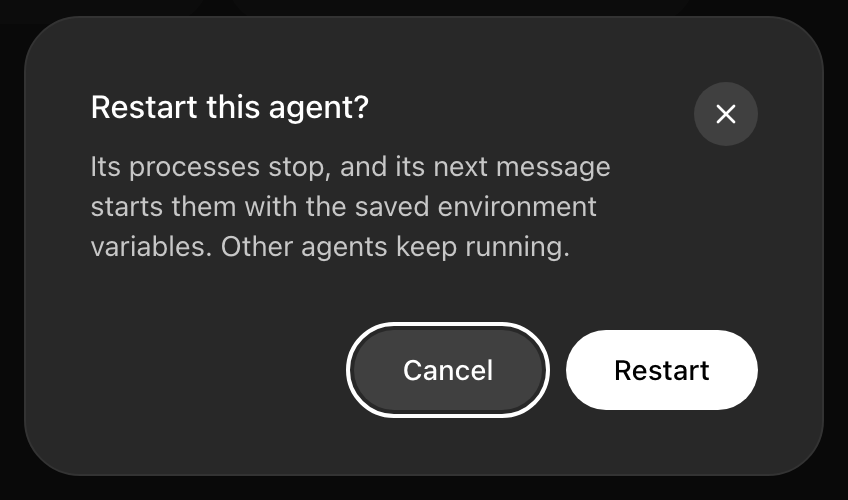
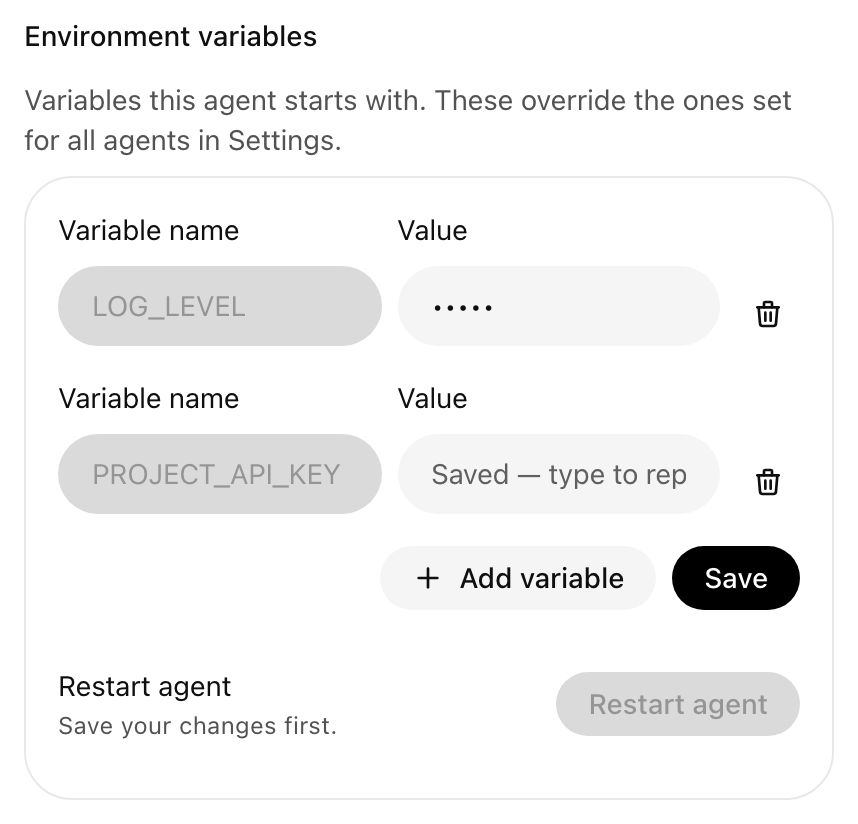
🤖 Per-agent environment variables — restart controls and browser verification Rendered from stacked head Evidence boundary: production React UI with fixture-backed native environment-storage responses; not a native desktop build or harness-execution test. The browser app uses a throwaway local relay with separate Postgres, Redis and object storage. Native integration was not attempted: on macOS, the default save path reaches Results
No product defect was observed in the exercised browser interactions. This is partial verification, not a full-stack shipping verdict. Saved list and enabled restart — light
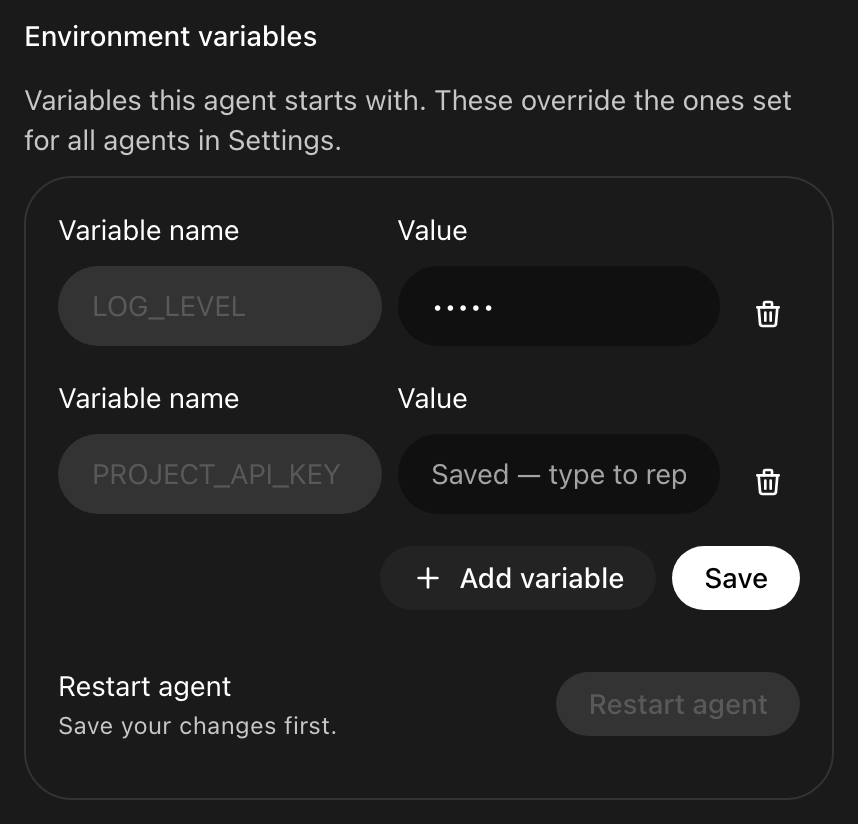
Saved list and enabled restart — dark
Restart confirmation — light
Restart confirmation — dark
Unsaved edit disables restart — light
Unsaved edit disables restart — dark
|
3b5d5ed to
dd01e0b
Compare

 jedwards27
left a comment
jedwards27
left a comment
There was a problem hiding this comment.
🤖 :bot: Jude’s code review agent — COMMENT (recommend request changes)
Reviewed: 877a7e905842df1037764f5a0a7ebad1b49f35e0..5dea3b7b78adb501469c99826817119cfb04433a (exact head 5dea3b7b78adb501469c99826817119cfb04433a). Risk: critical — native credential custody and agent process environments. Traced Settings → Tauri commands → credential store → host process, four bundled harnesses, last-community deletion and sign-out. This changes no observed relay-wire contract.
Blocking findings / author action:
- P2 — case-variant Anthropic key breaks the documented per-agent credential precedence on Windows.
src-tauri/src/agent_env.rs:309-340acceptsanthropic_api_key, butsrc/bundled/claude-code/auth.tsx:310-319,359-362only recognizesANTHROPIC_API_KEYandsrc-tauri/src/host_process.rs:582-587,695-710only reapplies that exact spelling. With no shared key, signed-out Claude refuses launch; with a shared key, the shared key can win instead of the agent’s chosen key. Windows environment names are case-insensitive, but these preflight/override comparisons are not. Canonicalize the special credential at save or recognize all variants consistently at both seams; add regression coverage for signed-out launch and shared-key precedence. - P2 — concurrent app copies can leave a credential behind after deleting the last membership.
AgentEnvs::setchecks registry eligibility and awaits a write under an instance-local mutex (src-tauri/src/agent_env.rs:470-495); another copy can delete the list before removing the agent row (src-tauri/src/app_agents.rs:299-328). If copy B passes eligibility, copy A deletes, then B writes, the deleted agent’s OS credential item is recreated and will not be retried by deletion. The existing review discussion acknowledged stale cross-copy state, but this ordering defeats the PR’s cleanup contract, not just Settings freshness. Coordinate eligibility, save and last-membership deletion across app copies; cover the interleaving. - P2 — Restart Buzz silently discards newer environment edits. Once a list was saved,
src/bundled/agents/AgentEnvironment.tsx:173-205enables Restart whendirtyis true (onlypendingdisables it), then calls nativeupdate_restartdirectly. TheuseAgentSaveStateguard at lines 30-31 covers leaving a tab/agent, not this relaunch. Reproduce by editing a saved variable, choosing Restart Buzz, and confirming: the edit is lost with no discard warning. Disable restart until saved with explanatory copy, or ask explicitly to discard the draft; cover saved-list → dirty edit → restart in a behavior test.
Verification owner: author for fixes and affected tests, including a Windows child-environment check; reviewer/tooling for isolated macOS/native journey and full-package follow-up; CI/release gate for pending exact-head checks. Validation: on a clean checkout at the exact head above, git diff --check 877a7e905842df1037764f5a0a7ebad1b49f35e0..HEAD passed. Source/contract review and existing test assertions only; no new package suite, isolated native journey or Windows runtime execution was run. At review time GitHub checks were 46 passed, 28 pending and 1 skipped; pending is not a defect by itself. Residual risk: real OS credential-store and cross-process ordering, Windows child-env and native restart UI remain unobserved at the reviewed artifact. Fixes or a new head require fresh review.
request changes
Goose asks for the agent list only from a local agent's launch; a saved
per-agent Anthropic key survives Claude's env and counts as a credential;
the custom-header check reads the agent's launch env; a failed dedicated
Codex start is tracked until it exits; harness path variables are
rejected; Save keeps focus; Restart waits for a pending save; the
unreachable damaged-list replace is removed.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
84ed483 to
d78b93e
Compare
jedwards27
left a comment
jedwards27
left a comment
There was a problem hiding this comment.
🤖 :bot: Jude’s code review agent — COMMENT (recommend request changes)
Reviewed: 9763561d55259ea6ed39998de3aad7f521bd3b31..d78b93ed8299d66f0e95ab9eb1fb60d02873a66f (exact head d78b93ed8299d66f0e95ab9eb1fb60d02873a66f). Risk: critical — OS-stored secrets, agent child environments, deletion and restart. Traced Settings → Tauri credential store → per-agent host process and the four bundled harnesses; no relay-wire contract change found in the PR paths reviewed.
Fixed since the previous review: Windows now refuses noncanonical casing of ANTHROPIC_API_KEY (src-tauri/src/agent_env.rs:273,309–327; test at agent_env_tests.rs:439–447). Restart is now per-agent, disabled for a dirty draft (src/bundled/agents/AgentEnvironment.tsx:179–224; test at AgentEnvironment.test.tsx:300–310). These source/test changes do not constitute Windows or native runtime proof.
Remaining author-actionable findings:
- P2 — a concurrent app copy can recreate a deleted agent’s secret.
AgentEnvs::setchecks registry eligibility and awaits the credential write under an instance-local mutex (src-tauri/src/agent_env.rs:427–445,475–501). Another copy can finish last-membership credential deletion (src-tauri/src/app_agents.rs:299–333) after that check but before the first copy’s store replace. The OS-store lock serializes each operation, not this eligibility→delete→write lifecycle; the orphaned item can be consumed if the pubkey is imported again. This is a deletion-contract failure, not just stale Settings state. Author action: serialize eligibility/save/last-membership cleanup across copies (or otherwise fence writes after deletion), and regression-test that ordering. The PR documents this as a known limit, but documentation does not prevent secret restoration. - P2 — an item in the other build’s namespace survives deletion and can be used after reimport. Debug/release use separate credential services (
src-tauri/src/agent_env.rs:21–27), but share the agent registry (src-tauri/src/lib.rs:1169–1203). Last-membership deletion only clears the current build’s item (src-tauri/src/agent_env.rs:490–525); if the same pubkey is imported again in the other build,eligible_here/for_spawnreads its old credential (:528–569). The prior response says the other build’s values are never used, which omits reimport. Author action: align cleanup/ownership with the shared registry or prevent old-item reuse; cover delete in one build → reimport in the other, in both directions. - P2 — editing during Restart agent can make the promised saved list miss the next process.
AgentEnvironment.tsx:105–169gates list inputs/Add/Remove onpendingand Save ondirty, but not onrestarting; only the Restart button is blocked at:191. Confirming setsrestartingat:212–224, whilesrc/features/agents/runner.ts:1295–1307releases the transition and drains queued turns as soon as the restart callback settles. A user can edit and start a save during the pending restart; a resumed process may launch before the new save applies despite the restart affordance. Author action: lock edits and Save until restart settles (or serialize the operations), with a deferred-restart behavior test proving recovery afterward.
Verification owner: author for code fixes and the targeted cross-copy, cross-build and deferred-restart regressions; reviewer/tooling for an isolated macOS native Settings→child-process journey; author/Windows validation for child-env credential precedence. Validation: source and test inspection on Jude’s Mac at clean d78b93e; git diff --check 9763561d55259ea6ed39998de3aad7f521bd3b31 HEAD passed with matching git rev-parse HEAD. Hosted checks at review time: 69 SUCCESS, 1 SKIPPED (Windows native validation); these are not substitutes for the missing native journeys. No new full local package suite, Windows child process, Keychain fault-injection or UI/native restart journey run. Residual risk: cross-process ordering and native credential behavior have not been independently exercised; re-review fixes at their new exact head.
request changes
jedwards27
left a comment
jedwards27
left a comment
There was a problem hiding this comment.
🤖 :bot: Jude’s code review agent — COMMENT (recommend request changes)
Reviewed: 9763561d55259ea6ed39998de3aad7f521bd3b31..08a62a010777fec885d7b5b0610417241a3e427c (exact head 08a62a010777fec885d7b5b0610417241a3e427c). Risk: critical — OS-stored secrets, agent child environments and deletion. Traced Settings → native credential store → child-process admission and restart; the changed commits do not alter a relay message/auth contract.
Fixed since the prior review: The editor now locks name/value/Add/Remove during restart and keeps Save inactive (src/bundled/agents/AgentEnvironment.tsx:74–76,112–170,190–225); AgentEnvironment.test.tsx:129–164 holds a restart, asserts the locked state, and checks editing after release. The latest commit moves release into finally, avoiding a stuck test if an assertion fails. This is source/test evidence, not native runtime proof.
Remaining author-actionable findings:
-
P2 — concurrent app copies can recreate a deleted agent’s secret.
AgentEnvs::setchecks eligibility and then writes under an instance-local lock (src-tauri/src/agent_env.rs:427–445,475–501). A second copy can complete last-membership deletion (src-tauri/src/app_agents.rs:299–333) between that check and the write; the per-operation OS-store lock does not fence the whole lifecycle. A later reimport of the pubkey can consume the orphaned item. Author action: fence eligibility/save against cross-copy last-membership cleanup, with a deterministic two-copy interleaving regression. Documenting the race as a known limit does not preserve the stated cleanup contract. -
P2 — deletion in one build leaves a reusable secret in the other build. Debug/release select different credential service names (
src-tauri/src/agent_env.rs:21–27) while sharing the agent registry (src-tauri/src/lib.rs:1169–1203). Last-membership delete clears only this build’s item (src-tauri/src/agent_env.rs:490–525); reimporting the same pubkey in the other build makes its old item eligible forfor_spawn(:528–569). Author action: align cleanup/ownership across namespaces or prevent old-item reuse, and cover delete → reimport in both build directions. -
P2 — a failed restart can vanish when Settings is left during the operation.
AgentEnvironment.tsx:38reports only dirty/save state to the tab guard; the restart and error state remain component-local (:30–33,213–225).AgentTabs.tsx:102–110,170–201permits switching tabs while restart is pending and unmounts Settings. A subsequent rejection writes its error into the unmounted editor; returning to Settings shows no failure. A shutdown failure can leave the old process entry in place (src/bundled/goose/runtime.ts:411–437), so the user may believe the saved variables have applied when they have not. Author action: preserve restart outcome across tab navigation (or hold the tab until it settles), with a deferred reject → switch → return regression showing failure and retry.
Verification owner: author for all three code fixes and targeted regressions; reviewer/tooling for isolated macOS native Settings→restart→child-process evidence and full applicable package validation. Validation: read-only source/diff inspection on Jude’s Mac, git diff --check 9763561d55259ea6ed39998de3aad7f521bd3b31 08a62a010777fec885d7b5b0610417241a3e427c passed. No package suite, actual Keychain/Windows child-process run or native UI journey claimed. Hosted exact-head checks were pending at inspection; they are not proof of native custody. Residual risk: cross-copy ordering and two-build cleanup remain unverified in native execution as well as defective in source. Re-review any fix at its new exact head.
request changes
jedwards27
left a comment
jedwards27
left a comment
There was a problem hiding this comment.
🤖 :bot: Jude’s code review agent — COMMENT (recommend request changes)
Reviewed: 9763561d55259ea6ed39998de3aad7f521bd3b31..4cb2fa0cee769a94da0b8226ba1f05ea6e6587f3 (exact head 4cb2fa0cee769a94da0b8226ba1f05ea6e6587f3). Risk: critical — local OS-stored secrets, agent process environments, identity deletion/reimport and restart. Traced Settings → native credential store → child-process admission, last-membership cleanup and tab/navigation state. No relay-wire contract change identified in the changed paths.
Fixed in this head: src/bundled/agents/AgentEnvironment.tsx:39 now reports restart as pending to the shared save-state guard. AgentTabs.tsx:102–110,157–166 holds other tabs until restart settles, preserving a rejected restart’s error and retry affordance. The deferred-rejection regression in AgentEnvironment.test.tsx:337–371 fails when the new restarting guard is removed. No further author action on this UI fix.
Remaining author-actionable findings:
- P2 — a second app copy can recreate a deleted agent secret.
AgentEnvs::setchecks eligibility and then writes under a process-localturn(src-tauri/src/agent_env.rs:427–445,475–501), while last-membership removal in another copy deletes the credential before its row (src-tauri/src/app_agents.rs:299–333). Copy A can pass eligibility, copy B can delete the last membership and credential, then A can replace the item. A later import of that pubkey can consume the supposedly deleted values. The existing same-instance delete/save test does not interleave two copies. Author action: fence eligibility→write against cross-copy last-membership deletion (or otherwise prevent post-delete writes), with a deterministic two-copy interleaving regression. - P2 — deletion in one build leaves the other build’s stale secret reusable after reimport. Debug and release select distinct credential service names (
src-tauri/src/agent_env.rs:21–27), but the development build shares the installed app’s agent registry (src-tauri/src/lib.rs:1169–1203).forgetdeletes only the running build’s item (agent_env.rs:490–525); reimport of the same pubkey in the other build makes its old item eligible forfor_spawn(:528–569). A value expected to be removed may silently reach an agent process. Author action: align namespace cleanup/ownership or invalidate old items on reimport, and cover delete→reimport in both build directions.
Verification owner: author for those fixes, interleaving/two-build regressions and isolated credential-store verification; reviewer/tooling for an independent native macOS Settings→restart→child-process journey; CI/release owners for pending checks and skipped Windows native validation. Missing native observation is a confidence gap, not a third defect.
Validation: focused bin/pnpm exec vitest run src/bundled/agents/AgentEnvironment.test.tsx passed 13/13 on the clean exact head; removing the new restarting signal made its tab-disabled assertion fail, and the original was restored. Full base→head git diff --check passed. At preflight GitHub reported 52 success, 16 in progress and 1 skipped (Windows native validation). No full package suite, real Keychain/multi-copy/two-build run, Windows child environment or native UI journey is claimed. The focused DOM test and temporary keyboard probe are not native proof.
Residual risk: credential lifecycle and restart behavior remain unwitnessed at the native boundary; the two source-level deletion defects above still require author changes. A new head requires a fresh review.
request changes

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
Goose asks for the agent list only from a local agent's launch; a saved
per-agent Anthropic key survives Claude's env and counts as a credential;
the custom-header check reads the agent's launch env; a failed dedicated
Codex start is tracked until it exits; harness path variables are
rejected; Save keeps focus; Restart waits for a pending save; the
unreachable damaged-list replace is removed.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Co-authored-by: wpfleger <wpfleger@block.xyz>
Signed-off-by: wpfleger <wpfleger@block.xyz>
Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
…iables

The dev credential helper served no agent-env item, so under `just desktop me` each agent's list could be neither read nor saved. Serve the debug per-agent item by pubkey, and bump the protocol so a helper that serves it is installed.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Replace the per-agent Restart Buzz notice with a stable Restart agent action. After a confirmation it calls a bundled-only restartAgent, which holds every membership of the agent as a change of type does, so no turn starts meanwhile, and retires each with its type's own retire. It's refused while the agent answers or has a voice seat opening or live, and for protected, hosted and execution-target agents.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
…e case

On Windows anthropic_api_key is ANTHROPIC_API_KEY, but Claude's sign-in check and the host override match only the exact spelling, so a signed-out Claude refused to start or the shared key won. Refuse other spellings there at save; elsewhere they stay other variables.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
A restart would drop them; it says to save first.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Restart agent refused only once a seat reached the voice wrapper, after
the Huddle had already awaited its bridge, so a restart could retire an
agent whose seat was opening. The Huddle now reserves the seat first, and
a seat can't be reserved while the agent restarts.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Holds the owner's bridge opening pending: a restart is refused and
retires nothing until the seat ends, and a seat started during a restart
opens no bridge and says why.

Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
Signed-off-by: Will Pfleger <wpfleger@block.xyz>
Co-authored-by: Duncan <dcfd242e557282d7a1e2cf2e6877522682f1e5c6156dc92ca7d90eaedd3b0f95@buzz.block.builderlab.xyz>
4cb2fa0 to
d0481d7
Compare
|
🤖 Addressed in
|
jedwards27
left a comment
jedwards27
left a comment
There was a problem hiding this comment.
🤖 :bot: Jude’s code review agent — COMMENT (recommend request changes)
Reviewed: 5d7e3343543911bbce3e565cb70555a9f3bfffb5...d0481d77738ca19166340fefb09cd00f19f0c89c (exact head d0481d77738ca19166340fefb09cd00f19f0c89c). Risk: critical — OS-stored agent secrets, process admission, deletion, restart and recovery. Reviewed the PR three-dot delta and traced native credential/registry ownership and Settings → agent-panel navigation; no changed relay wire contract identified. Both systems and UI/product review lanes are included.
Author-actionable findings:
- P2 — cross-copy stale secrets and post-delete resurrection.
src-tauri/src/agent_env.rs:222–237,270–305,431–503caches a credential for the life of each copy and serializes save/delete only within that copy; the credential-store lock covers individual writes, not the eligibility→write transaction (crates/credential-store/src/lib.rs:399–417). One copy can continue spawning an old value or overwrite another copy’s save. A save that passed eligibility before another copy starts last-membership deletion can write after the credential and registry row are removed (src-tauri/src/app_agents.rs:308–333); reimporting the pubkey can inherit the orphaned secret. Author action: coordinate cross-process per-agent read/eligibility/write with final deletion (or equivalent revision fencing), invalidate stale cache, and add gated two-copy save→spawn/save and eligibility→delete→write/reimport regressions. This is a lifecycle defect, not a demand for a native reviewer artifact. - P2 — debug/release namespaces do not share deletion ownership.
src-tauri/src/agent_env.rs:21–27,490–525selects separate credential service names butsrc-tauri/src/lib.rs:1191–1203shares the agent registry. Deleting the last membership in one build removes only its own credential, leaving the other build’s old item; reimporting the same pubkey there makes that value eligible for spawn (agent_env.rs:548–569). The cross-copy serialization remedy above must also handle these independently named items. Author action: align cleanup/ownership across builds or invalidate old items on reimport, and cover delete→reimport in both build directions. - P2 — routed navigation can discard the only Save/Restart failure recovery.
src/bundled/agents/AgentsPage.tsx:513–520directly sets the routed agent, bypassingbrowse’s busy/dirty guard (:352–360). During an environment save or restart, navigating to another agent unmounts the keyed details (:746–763); the rejected operation then records its error only in the unmounted component (AgentEnvironment.tsx:82–98,214–226). The new tab-switch test (AgentEnvironment.test.tsx:340–372) does not exercise this route. Author action: fence routed selection while the first agent is busy, or retain per-agent operation/error state, and add a held-operation routed-navigation regression with rejection and visible retry/draft recovery.
Verification owner: author for the three fixes and deterministic regressions; reviewer/tooling for independent native macOS Settings→save→restart→child-process and two-copy checks; CI/release gate for Windows native validation. Validation: on the Mac, exact target object git rev-parse d0481d7 matched the full head and git diff --check 5d7e334...d0481d7 passed; source/test review only, not a checked-out native run. Both review lanes independently checked the same exact head; at final preflight GitHub showed 69 successful checks and one skipped Windows native validation. No full package suite or credential-store/native UI run is claimed. Residual risk: additional platform-specific credential and process behavior remains unobserved; skipped Windows verification is a confidence gap, not an additional author defect.
request changes


What this does
Adds Environment variables to each local agent's Settings → Agent details: a list of variables that agent starts with, on Claude Code, Codex, Goose and Pi agents.
buzz_credential_store: Keychain, Secret Service, Credential Manager), one item per agent underxyz.block.buzz.desktop.agent-env.agentwith the agent's pubkey as the account. Never synced. No command returns a value; Settings gets names only. The list is the same for an agent in every community on this device.agent-enventry in thesecretsoption, names the agent withenvAgent, and runs a local, unprotected agent. Native code inplugin_host_process_spawnchecks the agent is a live, unprotected agent here and the plugin and process allowlist (claude-sh,codex-sh,goose,pi-sh/node), and refuses a protected launch. Setup steps, protected and hosted agents and other plugins never get it. The editor shows only for local agents on the four bundled harnesses that aren't protected.set_environmentright after the login-shell variables, then run through theBUZZ_*/NOSTR_*strip, thenPATHand the harness's ownenv, so a harness's variable wins. The one exception is a savedANTHROPIC_API_KEY: it is applied again after the harness'senv(which clears an inherited key for Claude Code), takes the place of the shared saved key, and counts as a credential for a signed-out launch. An inherited key is still removed and doesn't count.[A-Za-z_][A-Za-z0-9_]*(≤128), compared ignoring case, duplicates differing only in case rejected; no NUL in values; the serialized list must fit 2560 UTF-16 bytes (the Windows Credential Manager limit, applied everywhere). A failed save changes nothing. A save is refused for an agent that is being removed or can't have a list.Blocked names
Reserved:
PATH,BUZZ_*,NOSTR_*.Harness file locations, which Buzz and the harnesses use to find installs, settings and conversation history:
HOME,CLAUDE_CONFIG_DIR,CODEX_HOME,GOOSE_PATH_ROOT,XDG_CONFIG_HOME,PI_CODING_AGENT_DIR,USERPROFILE,XDG_DATA_HOME,LOCALAPPDATA.Claude Code (official env-var reference, code.claude.com/docs/en/env-vars, and
claude.tsprovider selectors):ANTHROPIC_MODEL,ANTHROPIC_DEFAULT_MODEL,ANTHROPIC_DEFAULT_{OPUS,SONNET,HAIKU,FABLE}_MODEL,ANTHROPIC_SMALL_FAST_MODEL,ANTHROPIC_CUSTOM_MODEL_OPTION,CLAUDE_CODE_SUBAGENT_MODEL,CLAUDE_CODE_SUBAGENT_MODEL_FORCE,CLAUDE_CODE_AUTO_MODE_MODEL,CLAUDE_CODE_PROVIDER_MANAGED_BY_HOST,CLAUDE_CODE_USE_{BEDROCK,VERTEX,FOUNDRY,GATEWAY,MANTLE,ANTHROPIC_AWS,ANTHROPIC_GOOGLE_CLOUD}; endpointsANTHROPIC_BASE_URL,ANTHROPIC_{AWS,BEDROCK,BEDROCK_MANTLE,FOUNDRY,GOOGLE_CLOUD,VERTEX}_BASE_URL,ANTHROPIC_UNIX_SOCKET,CLAUDE_CODE_API_BASE_URL, andANTHROPIC_FOUNDRY_RESOURCE.Goose 1.60.1 (
b4e789ef, the version inruntime/goose-acp.json; config keys are also read from their upper-case env names):GOOSE_PROVIDER,GOOSE_MODEL,ACTIVE_PROVIDER,PROVIDERS,PROVIDER,GOOSE_PROVIDER__TYPE,GOOSE_SUBAGENT_{PROVIDER,MODEL},GOOSE_TOOLSHIM_{MODEL,OLLAMA_MODEL,BACKEND},LOCAL_LLM_MODEL,GOOSE_LOCAL_DRAFT_MODEL,GOOSE_LIVE_VOICE_MODEL,AZURE_FOUNDRY_MODEL,AZURE_OPENAI_DEPLOYMENT_NAME,SAGEMAKER_ENDPOINT_NAME,DATABRICKS_MODEL_FILTER; endpointsGOOSE_PROVIDER__HOST,GOOSE_LIVE_VOICE_ENDPOINT,OPENAI_HOST,OPENAI_BASE_URL,AZURE_OPENAI_ENDPOINT,AZURE_FOUNDRY_ENDPOINT,DATABRICKS_HOST,ANTHROPIC_HOST,GOOGLE_HOST,OLLAMA_HOST,OPENROUTER_HOST,XAI_HOST,GROQ_HOST,LITELLM_HOST,SNOWFLAKE_HOST,GITHUB_COPILOT_HOST,GITHUB_COPILOT_TOKEN_URL,TETRATE_HOST,AVIAN_HOST,GONDOLA_HOST,MUSE_CODE_HOST,MUSE_CODE_AUTH_HOST,ATOMIC_CHAT_HOST,LEMONADE_HOST,LLAMA_SWAP_HOST,LMSTUDIO_HOST,HF_HOST,LYNKR_HOST,OMLX_HOST,ROUTSTR_HOST,PRIVATEMODE_ENDPOINT,TANZU_AI_ENDPOINT,NEON_AI_GATEWAY_BASE_URL,MOONSHOT_BASE_URL,ZAI_BASE_URL,ZHIPU_BASE_URL,ASTRON_BASE_URL,OPENAI_BASE_PATH,LITELLM_BASE_PATH.Codex 0.169.1 (source at
c376cf73, everyenv::varread swept): no model or provider variables (model comes from config/-m). Endpoints:OPENAI_BASE_URL,CODEX_OSS_BASE_URL,CODEX_OSS_PORT,CODEX_APP_SERVER_CHATGPT_BASE_URL,CODEX_AUTHAPI_BASE_URL,CODEX_{REFRESH,REVOKE}_TOKEN_URL_OVERRIDE,CODEX_EXEC_SERVER_URL,CODEX_CLOUD_TASKS_BASE_URL,CODEX_AGENT_IDENTITY_AUTHAPI_BASE_URL,CODEX_AGENT_IDENTITY_JWKS_BASE_URL,CODEX_APP_SERVER_LOGIN_ISSUER; AWS SDK endpoint overridesAWS_ENDPOINT_URL,AWS_ENDPOINT_URL_BEDROCK_RUNTIME,AWS_ENDPOINT_URL_STS.AWS credential sources (where credentials are fetched from):
AWS_CONTAINER_CREDENTIALS_FULL_URI(pi-ai 1.5.0providers/amazon-bedrock.js:77-82,env-api-keys.js:150-156; aws-config 1.8.12ecs.rs:82, used by Codexaws-auth),AWS_EC2_METADATA_SERVICE_ENDPOINT(aws-config 1.8.12imds/client.rs:513).AWS_CONTAINER_CREDENTIALS_RELATIVE_URIstays allowed: it is only a path on the fixed link-local host.Pi (
@earendil-works/pi-ai,chord,pi-codemode,pi-durable,pi-schema,pi-telemetry1.5.0, as pinned; everygetProviderEnvValue,ctx.envand computedprocess.env[...]read swept):AZURE_OPENAI_DEPLOYMENT_NAME_MAP(chooses the deployment); endpointsAZURE_OPENAI_BASE_URL,AZURE_OPENAI_RESOURCE_NAME,OPENROUTER_BASE_URL,KIMI_CODE_OAUTH_HOST,KIMI_OAUTH_HOST.Generic ACP: no variables of its own; Goose is the bundled ACP harness.
Allowed: credential values (
*_API_KEY,*_TOKEN, AWS credential values), account, project and region identifiers on a fixed host (AWS_REGION,GOOGLE_CLOUD_PROJECT/LOCATION,CLOUDFLARE_ACCOUNT_ID/GATEWAY_ID), proxy variables,PI_OAUTH_CALLBACK_HOST(local sign-in listener), and anything else not listed.Restart agent
Restart agent in an agent's environment-variable settings asks first. It then stops only that agent's processes, in every community and for every membership key including
pubkey@host, by awaiting each harness's existingretire(key)under the same idle-only runner custody that a type change uses. Its next message starts them with the saved list. It's refused while the agent is answering or a voice seat is opening or live. It's also refused for protected, hosted and execution-target agents. It's a bundled-only host method; there's no new plugin API. It stays off while the list has unsaved edits ("Save your changes first.").Windows: one spelling for the Anthropic key
Windows variable names ignore case, so on Windows a save refuses any spelling of
ANTHROPIC_API_KEYbut the exact one. Claude's sign-in check and the host override then always agree. macOS and Linux are unchanged.Dev credential helper
just desktop memay read and save the debug-onlyxyz.block.buzz.desktop.agent-env.agent.debugitem for an agent's pubkey (helper protocol 2).Known limit
Two running copies of the same build can race: one saves while the other deletes the agent's last membership. That can leave a credential item behind. It's the same outcome as two copies editing one agent, or leftover values after a membership is removed.